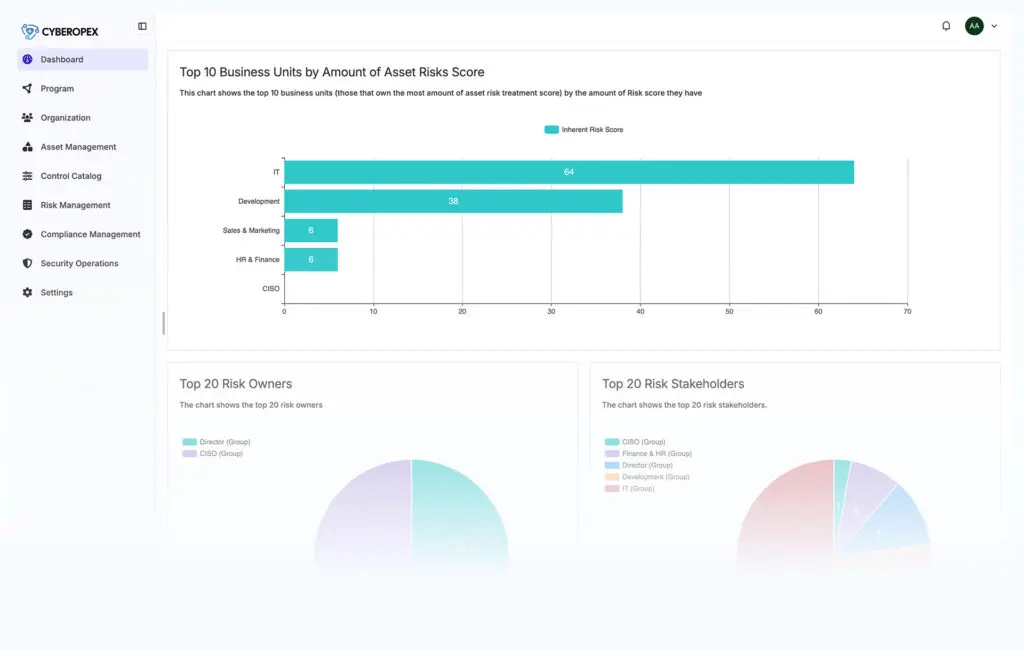
Governance
Set strategic guardrails
Define and manage policies centrally, assign clear responsibilities and align business goals with regulatory standards.
Governance, risk and compliance in one platform. Built-in AI agents automate routine tasks so you can focus on your business: secure, legally compliant and hosted in Switzerland.
Define and manage policies centrally, assign clear responsibilities and align business goals with regulatory standards.
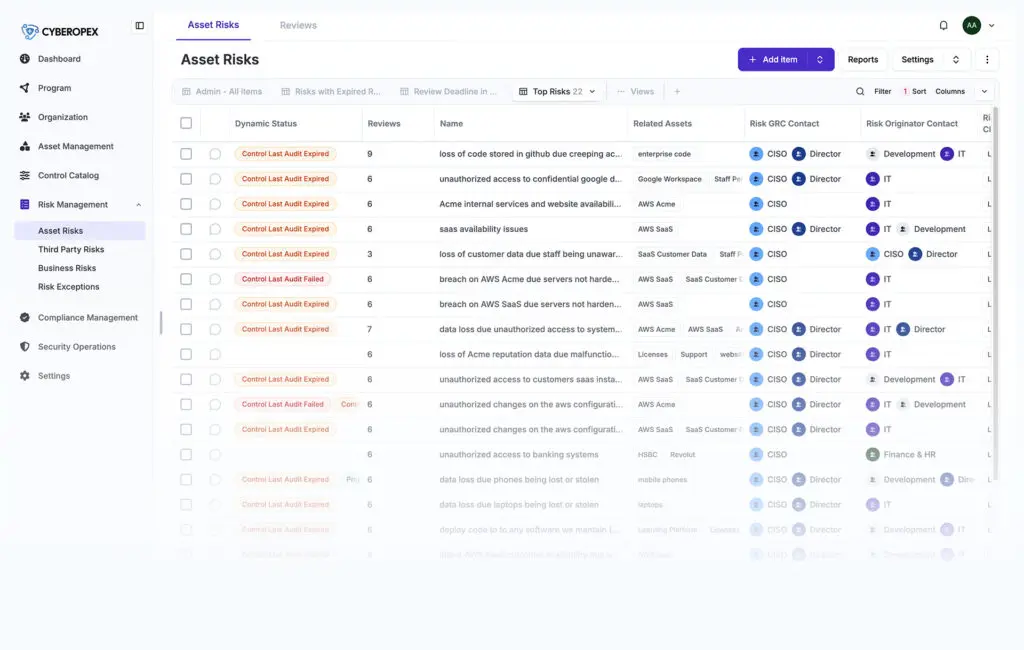
Identify, assess and prioritise risks in real time. Scoring models and alerts make uncertainty measurable.
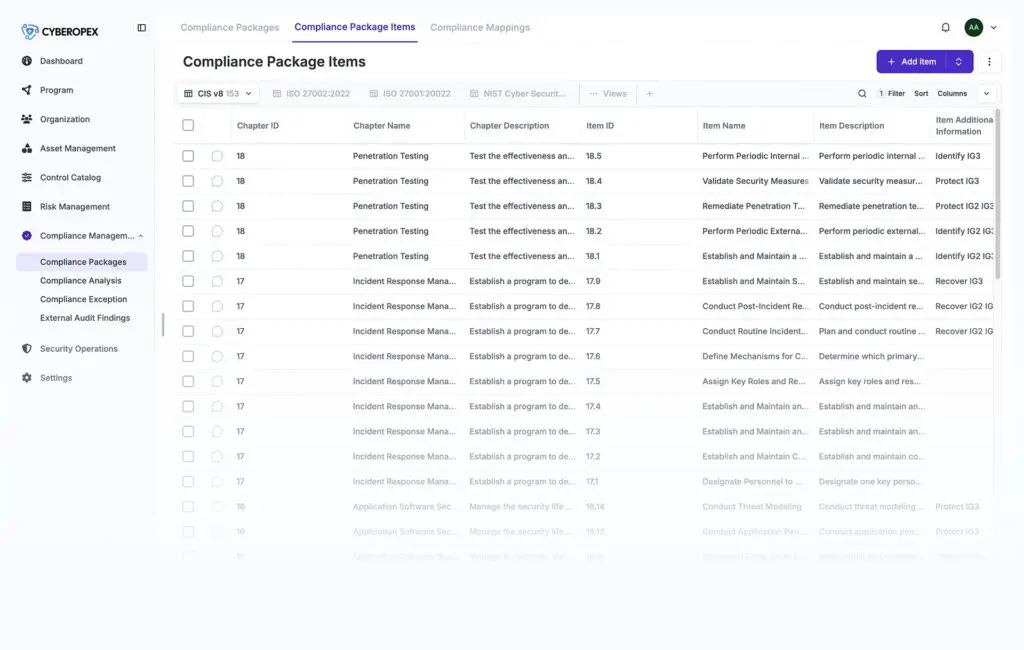
Monitor GDPR, revFADP (revDSG), ISO 27001 or NIS2 without gaps. Checklists and status reports show your level of compliance at any time.
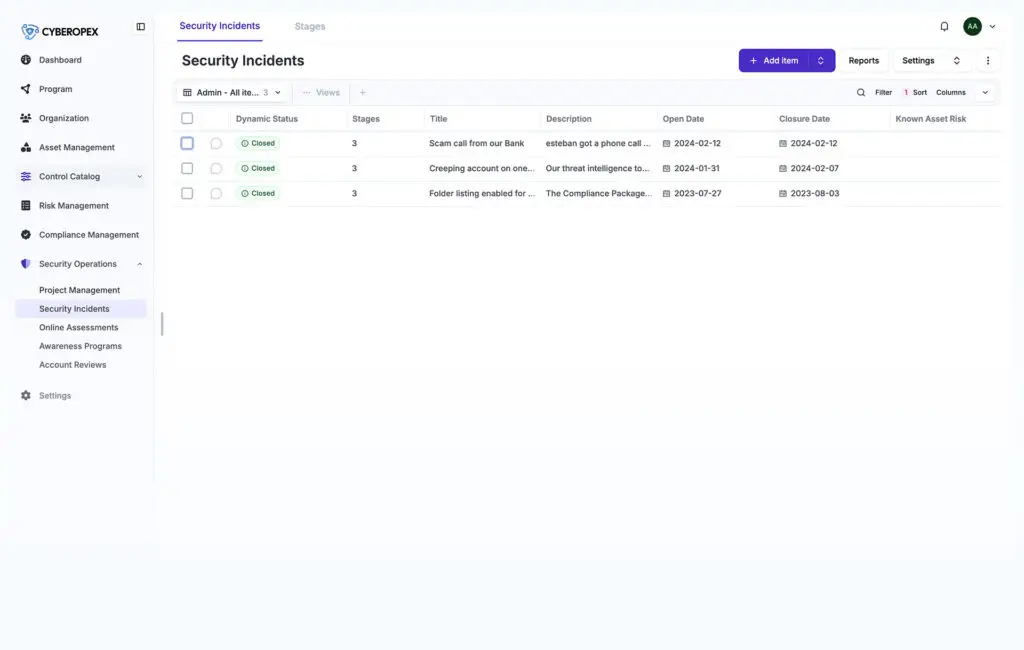
Document and manage security incidents systematically. Workflows help you take the right measures straight away.
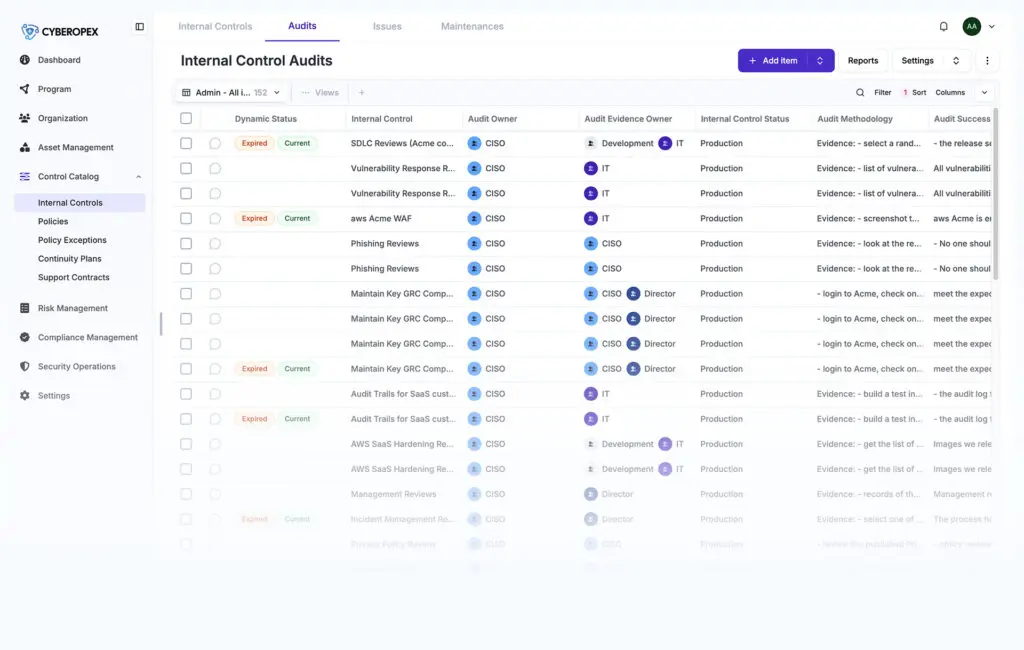
Audit-proof reports and evidence at the click of a mouse. All required documents are immediately to hand.
“Your ISMS runs, even without an ISMS team.”
We run your information security management system on our Eramba-based GRC platform. It is hosted in Switzerland, in an ISO 27001-certified data centre.
Reviews evidence like an internal auditor and recommends: accept, reject or ask for more.
Assesses control design and effectiveness and makes test requirements measurable.
Reviews scenarios and ratings, evaluates online assessments and proposes treatment.
Reviews policies against ISO 27001, NIS2 and the revFADP and shows gaps with a text proposal.
Evaluates supplier questionnaires and certificates and proposes a rating.
Checks audit readiness according to ISO 19011 and drafts findings with actions.
Turns the pentest report into a tracked remediation plan with a management report.
“Compliance is not a brake but a decisive competitive advantage.”
Define standards, scope and owners.
We provision your instance in a data centre in Switzerland: hardened, with backups and monitoring.
Sign-in with your Microsoft account, roles and predefined mappings for your standards.
We migrate your existing policies, risks and measures from Excel or Word for you.
Updates, monitoring and, if you wish, ISMS operation by us. You can add AI agents at any time.
A GRC tool (governance, risk, compliance) brings policies, risk management and compliance with legal requirements such as the revFADP, GDPR, ISO 27001 or NIS2 together in one place. Without a central system, this information is spread across Excel lists and folders. That makes audits laborious and gaps invisible.
The platform runs in an ISO 27001-certified data centre in Switzerland. Data is encrypted at rest and in transit. Access is role-based and protected with multi-factor authentication. Your compliance data is never used to train public AI models.
Yes. We supply predefined mappings for ISO 27001, NIS2, revFADP, GDPR, NIST CSF, CIS, BSI IT-Grundschutz, TISAX and ISO 42001. So you do not start from zero.
Swiss GRC Hosting is the product: your own platform at a fixed price. GRC as a Service is the package around it: set-up, data migration, ISMS operation by us if you wish, and AI agents.
We use standard interfaces (APIs), for example to Microsoft 365, SAP or Salesforce. Integration is usually done within a few days.
Write to us. We will show you the platform in a short demo.