We make Swiss companies cyber-resilient.
Cyberopex advises, implements and operates: from NIS2 and ISO 27001 to AI governance and AI security under ISO 42001 and ISO/IEC 27090. With experienced consultants, our own GRC platform and AI agents. Hosted in Switzerland.
Companies and organisations that trust Cyberopex
One partner for strategy, technology and operations.
We analyse your security posture and develop concepts and measures that fit your systems. We then implement them or run them for you, aligned with legal and technical standards.
Cyber Security Consulting
Cyber security, resilience against cyber risks, governance, risk management and compliance, digitalisation or cloud security: we bring structure to your information security and make it audit-ready.
Managed Services
We run your ISMS, lead your security and train your staff on an ongoing basis. Your team can focus on day-to-day business.
AI Governance & AI GRC agents
We help you use AI securely and in compliance with the rules, and we use AI ourselves to make your ISMS more efficient.
AI & Engineering: infrastructure, agents and smart home
We build your own AI platform in Switzerland and develop AI agents that work within your processes. Vendor-independent and secure from the start.
Your GRC platform. Hosted in Switzerland.
Run it yourself or have it run for you: you get your own Eramba instance in an ISO 27001-certified data centre in Switzerland. On request, we also run your ISMS.
Top risks
Upcoming reviews
Sample view with demo data
Swiss GRC Hosting
- Your own Eramba instance for your ISMS
- Hosting in Switzerland, ISO 27001-certified data centre
- Updates, backups and monitoring included
- Single sign-on via SAML
- AI agents as an add-on for CHF 590.– / month
Prefer to have it run for you? GRC as a Service
Everything in Swiss GRC Hosting, plus setup and support by our consultants. Want us to run the whole ISMS? That is Managed ISMS.
- Setup & data migration
- Support by GRC consultants
- AI agents for routine work
- Audit preparation & reporting
Six AI agents for your ISMS
Evidence review, control review, risk analysis, policy review, vendor risk and audit readiness. Pentest governance follows in January 2027. CHF 590.– per agent per month, 50 agent runs per month included, then CHF 0.70 per run, excl. VAT.
- Human in the Loop
- Data stays in Switzerland
- Savings calculator
Security starts with people.
Would you like training for your team? We can help in these areas:
 GRC platform
 Copilot, Agent 365, Purview
 Security Monitoring
 Open-source GRC
Which rules apply to your company?
Four questions, a first assessment: NIS2, revFADP and GDPR, ISA reporting obligation, ISO 27001 or AI regulation. In 30 seconds.
Your assessment
Based on your answers, these topics are relevant:
Recommendation: NIS2 gap analysis with an ISO 27001 roadmap.
Book a callApplies: mandatoryCheck: depends on your activitiesRecommended: voluntary standard
Initial guidance only. It does not replace a legal review of your specific case.
What we have achieved for our clients.
Hands-on projects from medtech, industry, security and food tech. Read how we approached them and what they delivered.
 Governance
ISMS & GRC with the canton of Glarus
ISMS under ISO/IEC 27001:2022 and a GRC tool for the administration, municipalities, courts, police and schools.
Read case study Governance
Security governance with Haag-Streit
A security governance framework based on NIST for the strict requirements of medtech.
Read case studyIntegrationSOC support with Haag-Streit
Faster incident handling and proactive threat hunting with Microsoft Defender and Sentinel.
Read case study Consulting
Cyber Security Officer service with V-ZUG
An external Cyber Security Officer for a leading Swiss manufacturer of household appliances.
Read case study Integration
Information security and ICT with AEB
Security as a whole: concepts, systems engineering and new technologies, on-prem and in the cloud.
Read case study Assessment
NIST security assessment with Planted
A fast status assessment based on NIST, with first improvements during the audit itself.
Read case study Awareness
Phishing campaign with Hortima
Simulated phishing attacks so that staff reliably recognise fraudulent emails.
Read case studyTrainingSecurity awareness with Hortima
Training that builds a strong security culture across the whole company.
Read case study Consulting
Test management assessment with Kanadevia Inova
Test processes assessed and benchmarked against ISO/IEC/IEEE 29119, ISTQB and TMMi: clear measures for quality and efficiency.
Read case study Integration
Secure Your Modern Workplace with smart.t
Security assessment of Microsoft 365, Entra ID and endpoints, followed by hardening with Defender, Conditional Access and Intune.
Read case studyBecome our next case study.
Tell us where you stand. We will show you how we would approach it.
Arrange a callOver 30 companies trust Cyberopex.
From medtech and industry to the public sector: this is what our clients say about working with us.
All case studiesNews from security, GRC and Microsoft.
Practical knowledge from our projects: short, concrete and tailored to Swiss companies. View all articles
ISO/IEC 27090: Security for AI systems
What the new standard says about data poisoning and model theft, and how it fits with ISO 27001 and ISO 42001.
Read articleCopilot rollout: permissions first
Copilot shows everything a user is allowed to see. That is why permissions, labels and DLP need a review before the rollout.
Read articleGRC as a Service: evidence instead of Excel lists
Why an Excel-based ISMS reaches its limits with an audit, a NIS2 request or a report to the National Cyber Security Centre / Federal Office for Cybersecurity (BACS), and how a GRC platform helps.
Read article Podcast · every TuesdayCyberopex BriefingCyber security, GRC and AI in plain language, with Christian Serra. In German and English.
 Free for childrenProfessor AlessioLearning videos for children aged 2 to 10, new every week on YouTube.
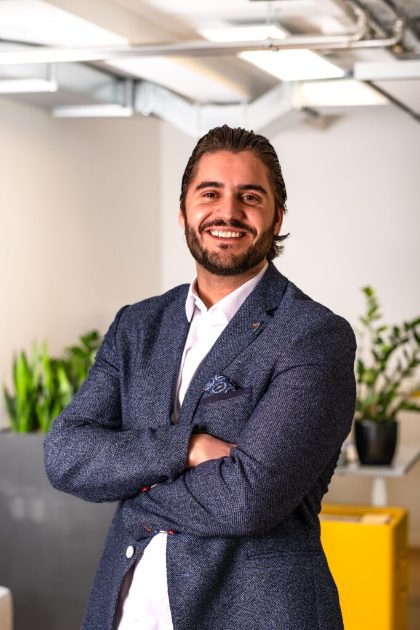
Pioneers in cyber security, governance and AI.
Since 2020 we have combined consulting, our own GRC platform and AI agents from a single source for Swiss companies of every size.
Our vision: every Swiss company can use AI and digitalisation securely, with an ISMS that runs day to day, even without its own ISMS team.
Founder and expert in cyber security, governance and AI, with 20 years of experience in IT. Christian Serra combines strategy and technology: he builds ISMS and governance programmes based on ISO 27001, ISO 42001, ISO/IEC 27090, NIS2, NIST CSF and revFADP, advises executive boards on the secure use of AI and, with his team, builds AI infrastructure and AI agents for companies.
Frequently asked questions
Is your question not listed? We usually reply on the same working day.
Does NIS2 also apply to Swiss companies?
NIS2 applies directly only in the EU. However, Swiss companies are affected if they have branches or services in the EU or supply critical EU customers. We clarify your scope in a short analysis.
What does an ISO 27001 implementation cost?
That depends on size, scope and maturity. In a short initial consultation, we estimate effort and budget. For ongoing operation, Swiss GRC Hosting is available from CHF 5'990.– / year.
What is GRC as a Service?
We set up your own GRC platform in Switzerland, migrate data and controls and run the platform, with AI agents if you wish. Your team does the ISMS work. If you want us to take that on too, there is Managed ISMS.
Does Cyberopex also build AI solutions for us?
Yes. With AI Engineering we build your own AI infrastructure in Switzerland and develop AI agents for marketing, sales, customer service and administration, secured under ISO/IEC 27090.
Where is our data stored?
Exclusively in Switzerland. Cyberopex operates the platform and the AI agents in an ISO 27001-certified data centre in Switzerland.
Do you also work with smaller companies?
Yes. Our services are also tailored specifically to SMEs, because every company should be able to afford strong cyber security.
How can we help?
Tell us briefly what it is about. We will get back to you with a proposed date for a no-obligation initial consultation.